By Rehan Khalid · TechHubMe
To protect client data when using AI productivity tools, use an approved work account, submit only the minimum authorized information, check data-use and retention settings, restrict connected sources, and review the output before sharing it. Keep passwords, API keys, and unapproved confidential records out of prompts and uploads.
This guide helps small teams turn those safeguards into repeatable approvals, access controls, review steps, and an incident-reporting process. Approval depends on the service, account, settings, information involved, and client commitments; no single privacy toggle makes every use appropriate.
Start with approved tools and minimal client data
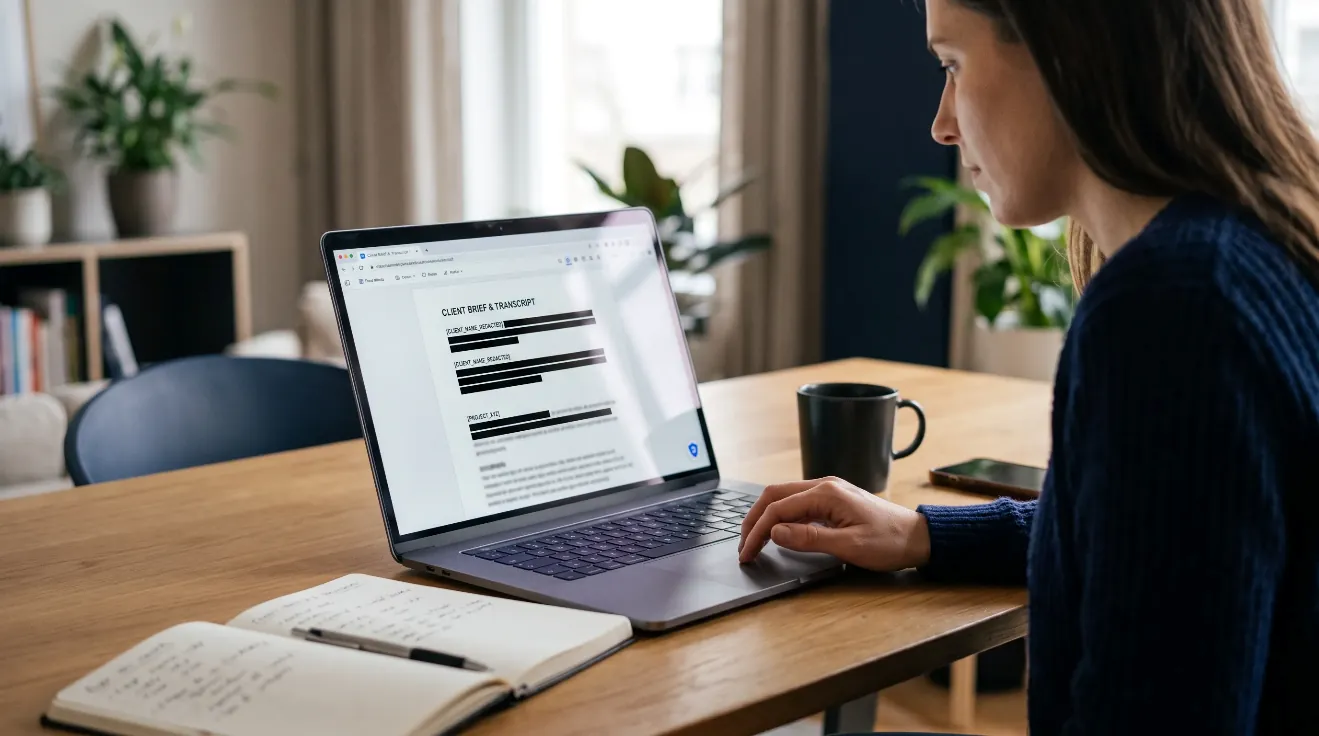
Approval belongs to a particular tool, account, configuration, and use case. Your organization's client commitments also matter, so permission to draft public marketing copy doesn't automatically authorize uploading client records.
Know what to keep out of prompts and uploads
Keep client names and contact details, health or financial records, contracts, private emails, and confidential plans out of unapproved tools. Never include passwords or API keys in ordinary productivity prompts.
Follow confidentiality agreements, privacy requirements, and sector-specific obligations. For example, permission to handle health information internally doesn't authorize sending it to another service.
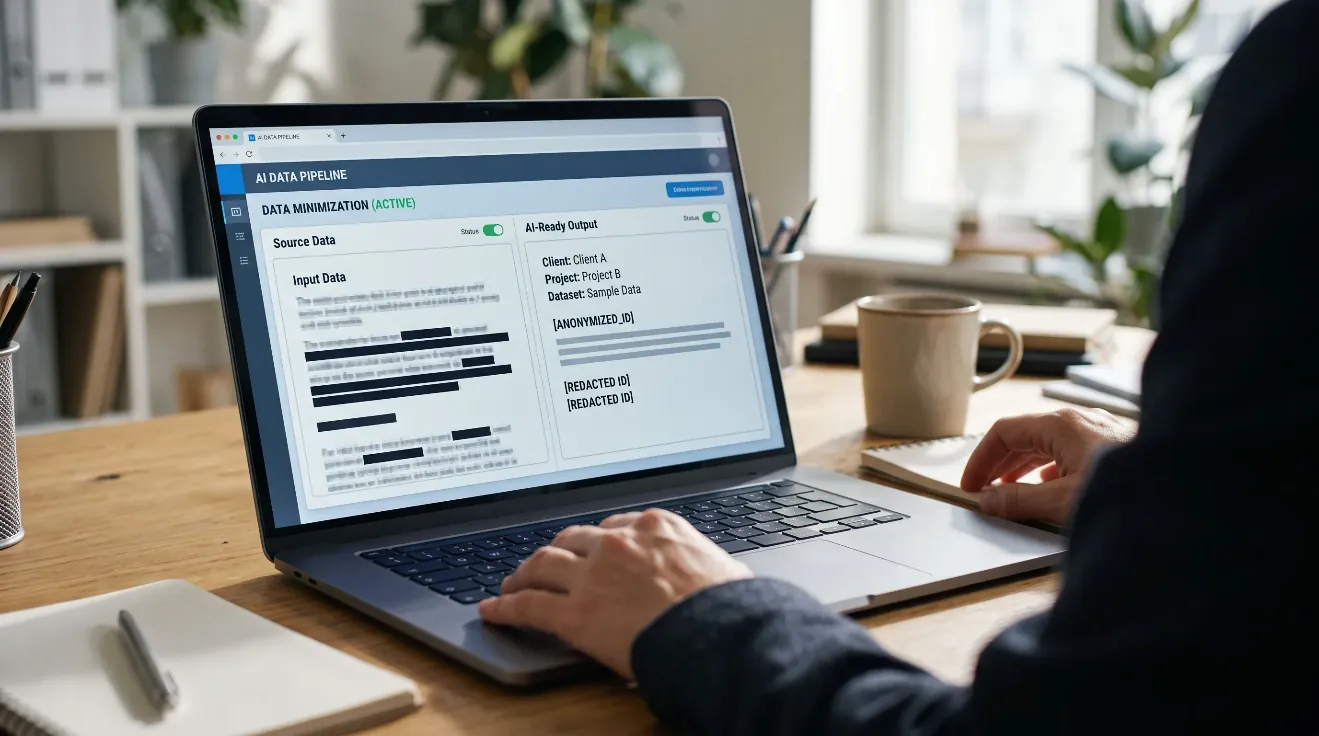
Remove identifiers and unnecessary details before submission. However, removing names alone may leave someone identifiable through dates, job titles, or unusual circumstances. These generative AI privacy risks extend beyond obvious personal identifiers.
Use a simple safe-prompt workflow
Apply the same sequence each time:
- Sign in through your approved work account.
- Reduce the input to the minimum necessary.
- Ask for a narrowly defined task.
- Include only authorized files and connected sources.
For a project update, request clearer wording using nonconfidential text instead of pasting the client's full email thread. Keep attachments and unrelated conversation history outside the prompt.
Example of a safer prompt
Avoid: "Summarize the attached client email chain, contract, contact list, and invoice details."
Use instead: "Rewrite this approved, nonconfidential update in three clear sentences: Project A has completed its design stage. Testing starts next week. The next update is due Friday. Do not add facts."
Use placeholders only when the remaining context is also safe to share. For individual project work, see our AI workflow guide for freelancers.
Check AI privacy settings and access before sharing client data
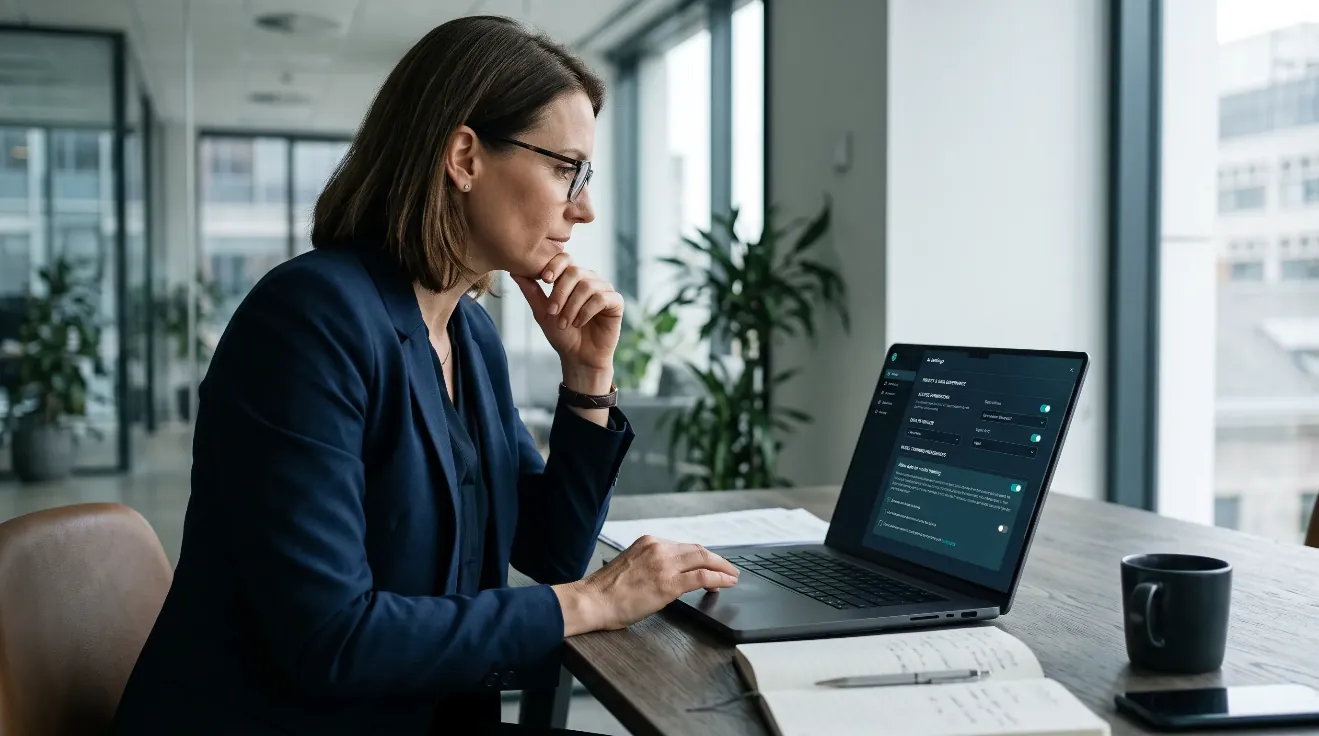
Personal accounts and business plans can operate under different terms. Document the approved configuration and permitted data categories before employees use the service. A productivity tool evaluation checklist helps make those decisions consistent across teams.
Confirm data use, retention, and account controls
Your approval record should address model training, retention periods, human access, and administrator audit or deletion capabilities. Assign someone responsibility for maintaining that record when settings or product features change.
According to Microsoft's Copilot privacy documentation, commercial Microsoft 365 Copilot prompts, responses, and Microsoft Graph data aren't used to train foundation language models. Copilot activity history can still store prompts and responses.
Apply the protections associated with your organization's actual work-account terms and settings. Training restrictions and retention controls address different risks.
Limit access to connected files and apps
Grant access only to sources needed for the task. Review shared links and group memberships, label sensitive documents, and apply available data-loss prevention and audit controls.
An assistant may surface information its user already has permission to access. As a result, broad folder permissions can expose material employees wouldn't otherwise encounter.
Connecting AI to a poorly restricted document library gives existing access problems another route into everyday work.
Before connecting a shared workspace, apply the same permission checks used for sharing client files securely: restrict recipients, avoid public links, and remove access when it is no longer needed.
Review AI output and prepare for mistakes or data exposure
Use NIST's AI Risk Management Framework as a practical structure: Govern assigns responsibility, Map identifies exposure, Measure evaluates safeguards, and Manage addresses risks. Give each activity a named owner.
Verify summaries before sharing or acting on them
AI can invent details, misread source material, or repeat restricted information that should not be shared outside an approved audience. A qualified employee should compare every summary, recommendation, or generated document with the original sources before anyone relies on it. This review should check facts, figures, dates, names, legal references, and conclusions to ensure the output is accurate, complete, and appropriate for its intended purpose.
Remove unnecessary client details before sharing any AI-assisted result, and confirm that every recipient is authorized to receive the information. Treat generated documents according to their contents, including confidential facts carried over from approved inputs, rather than assuming that an AI-generated file is automatically safe to circulate. A polished response still needs human judgment before it supports a client decision, especially when it involves legal, financial, medical, contractual, or regulatory matters.
Know what to do if sensitive data is exposed
If sensitive information is exposed through an AI tool, stop sharing it immediately and notify your organization’s privacy, security, or IT lead through the approved reporting process. Preserve key details, such as the tool used, account involved, submission time, affected files, and any known recipients, so the incident can be assessed accurately.
Follow the official incident-response plan instead of using more AI prompts to investigate or delete the information. Additional prompts may create new copies of the data or interfere with the investigation, so leave containment and evidence handling to the designated response team.
Legal, contractual, and client-notification requirements depend on the type of data exposed and the applicable rules. Let the responsible team determine the next steps, while you document what happened and avoid sharing details outside the approved response channel.
Frequently Asked Questions
Does client consent authorize any AI use?
Consent doesn't remove contractual restrictions or other legal duties. Your organization still needs an approved purpose, appropriate safeguards, and authority to share the information with that service.
Are offline AI tools a safer option?
Offline processing can reduce external transmission, but local files and device access still need protection. Software that runs locally also needs controls for stored conversations, backups, and any enabled network connections.
Can browser extensions access client information?
An extension's permissions may allow access to webpage content or other browser data. Require organizational approval before installing AI extensions in browsers used for client work.
Should freelancers follow the same AI rules?
Yes, anyone handling client information should follow the applicable confidentiality and AI-use requirements. Put permitted uses and reporting responsibilities in their written working instructions before sharing access.
How can you ensure data privacy with AI?
Collect only the information needed for an approved task, limit access, and use appropriate encryption and retention controls. Remove unnecessary identifiers, document data flows, and review the service before deployment. Pseudonymized records may still identify someone when combined with other details.
How can you protect your personal data when using AI tools?
Share only the information necessary for an approved task. Avoid passwords, identity documents, financial or health records, private photos, and other sensitive details in unapproved services. Where available, review model-training preferences separately from chat-history and retention settings. Deleting a visible conversation does not necessarily remove all provider-held copies immediately; check the applicable policy.
Make Client Confidentiality a Daily AI Habit
Use approved tools and settings, share the minimum information needed, and review every output before it leaves your team. These habits protect confidentiality throughout the workflow, including after the AI produces an answer.
Turn them into a short written policy that employees and contractors can follow. When a task falls outside that policy, ask your security or privacy lead before submitting client information. To place these safeguards within a repeatable process, use our AI productivity workflow guide.